
Linux TCP flaw gets RHEL patches while Ubuntu LTS fixes remain in testing
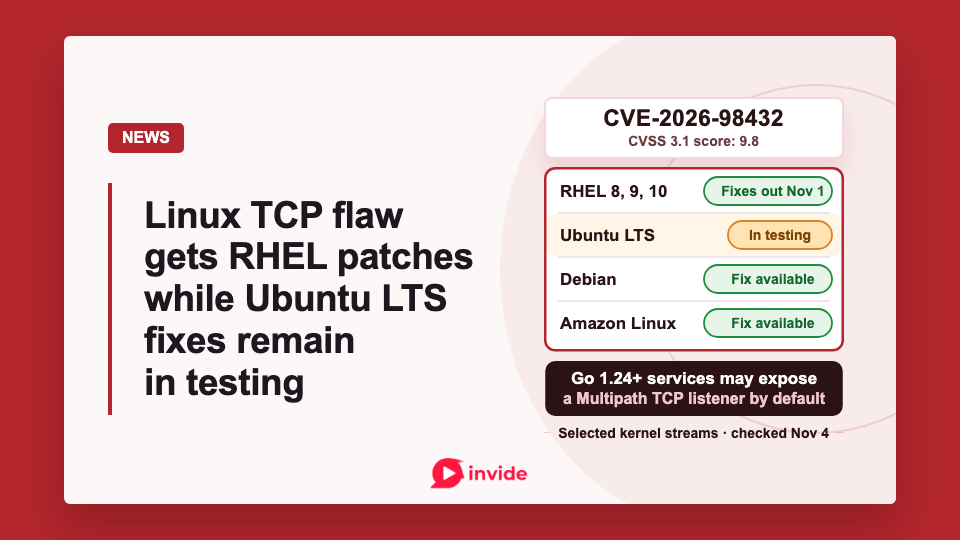
Red Hat issued kernel updates for RHEL 8, 9 and 10 on November 1 to fix CVE-2026-98432, a vulnerability in Linux's IPv4 TCP connection handling (RHSA-2026:93414, 93412, 93413).
As of November 4, Ubuntu's main LTS kernel fixes remain in testing. Canonical's November 2 update says users who perform their own kernel acceptance tests can install them from the opt-in -proposed channel. Regular updates will follow Canonical's validation.
The vulnerability has a CVSS 3.1 score of 9.8, rated Critical by Ubuntu. Anthropic has reported remote command execution as root against a server with a Multipath TCP listener.
How the bug works
The attack requires a TCP connection request carrying IPv4 options in its SYN packet. The kernel can free memory containing those options while another processor still reads it to prepare a handshake reply. A retransmitted request can trigger the race. Request socket migration can also trigger it, but only when net.ipv4.tcp_migrate_req=1 is set or a BPF_SK_REUSEPORT_SELECT_OR_MIGRATE program is attached. The resulting use-after-free can expose kernel memory, corrupt memory or crash the system.
The flaw dates to Linux 4.4 and remains in kernels that lack the fix. The upstream patch delays freeing the options until concurrent readers have finished.
In its October 27 research report, Anthropic said Claude wrote an exploit after initial prompting. Against a Linux server with a Multipath TCP (MPTCP) listener, it first leaked a kernel pointer to bypass address randomization, then used the same bug to run a shell command as root. No credentials or user interaction were required. Its proof of concept took 48 minutes for the leak and another five for command execution. Losing the race only failed the handshake, allowing repeated attempts.
Anthropic's exploit remains unreleased, according to Canonical. AWS said in its security bulletin that it had no evidence of exploitation. Akamai's November 2 analysis reported no known public working exploit.
Where patches are available
The following status was checked on November 4. Specialized kernel packages and extended-support streams need their own advisory check.
| Distribution | Verified status |
|---|---|
| RHEL 8.10 | kernel-4.18.0-553.182.1.el8_10 includes the fix. RHSA-2026:93414. |
| RHEL 9.8 | kernel-5.14.0-687.64.1.el9_8 includes the fix. RHSA-2026:93412. |
| RHEL 10.2 | kernel-6.12.0-211.72.1.el10_2 includes the fix. RHSA-2026:93413. |
| Ubuntu 22.04, 24.04 and 26.04 LTS | Generic linux fixes are in -proposed. Canonical lists versions 5.15.0-203.213, 6.8.0-149.149 and 7.0.0-43.43, respectively. Older supported releases await fixes. See Canonical's rollout update. |
| Debian Bookworm and Trixie | The first fixed linux source versions are 6.1.190-1 and 6.12.113-1, respectively. Use those or later security updates. Bookworm's linux-6.12 package is fixed in 6.12.113-1~deb12u1. Debian tracker. |
| Amazon Linux 2 and 2023 | Fixed kernel packages are available. Release-pinned AL2023 instances need release 2023.12.20261102 or later to receive the updated kernel, according to the AWS bulletin. |
RHEL 8's real-time kernel also has a fix in RHSA-2026:93415. Red Hat's November 4 VEX record still lists OpenShift's RHCOS components as affected.
For self-built kernels, the Linux CVE announcement lists the first fixed releases on their respective branches: 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10 and 7.3. Distribution kernels with backports use their vendors' package versions.
Check Go listeners and the kernel you boot
The Go Security Team warned on October 29 that Go 1.24 introduced MPTCP enabled by default for Linux listening sockets. With kernel support and MPTCP enabled, a Go service can expose the listener used in Anthropic's demonstration without explicitly opting in. Go's defaults also depend on the module's declared Go version and explicit overrides, so the compiler version alone cannot establish exposure.
The underlying flaw affects ordinary IPv4 TCP handling too. Red Hat explicitly warns that its default configuration remains vulnerable even though MPTCP is disabled.
The immediate steps are:
- Install the fixed kernel for the exact distribution stream and reboot. Ubuntu's
uname -rreports the booted kernel's ABI; use Canonical'sdpkg -l 'linux-image*'listing to find the full installed package version for that ABI before comparing it with the table. - For Go services awaiting a patch, restart with
GODEBUG=multipathtcp=0in the environment, or rebuild withgodebug multipathtcp=0in the main module'sgo.mod, orgo.workfor workspace builds. Per-socketSetMultipathTCPcalls override that setting. Disabling MPTCP per program leaves the underlying kernel bug unresolved. - Test Red Hat's interim filter against required traffic before relying on it. It drops IPv4 TCP packets with IP options while permitting standard TCP-header options, but cannot fully prevent exploitation. Connections that require IP options may break. The rule does not survive a reboot. Reapply it after any reboot until a fixed kernel is running. On OpenShift, a host rule does not filter pod-to-pod traffic inside the cluster network.
Ubuntu LTS users considering -proposed need their own kernel acceptance tests. Canonical has not given a date for regular updates; its security team says security updates are the only appropriate mitigation.
Member discussion