
NGINX fixes two HTTP/2 flaws. Which build should you update to?
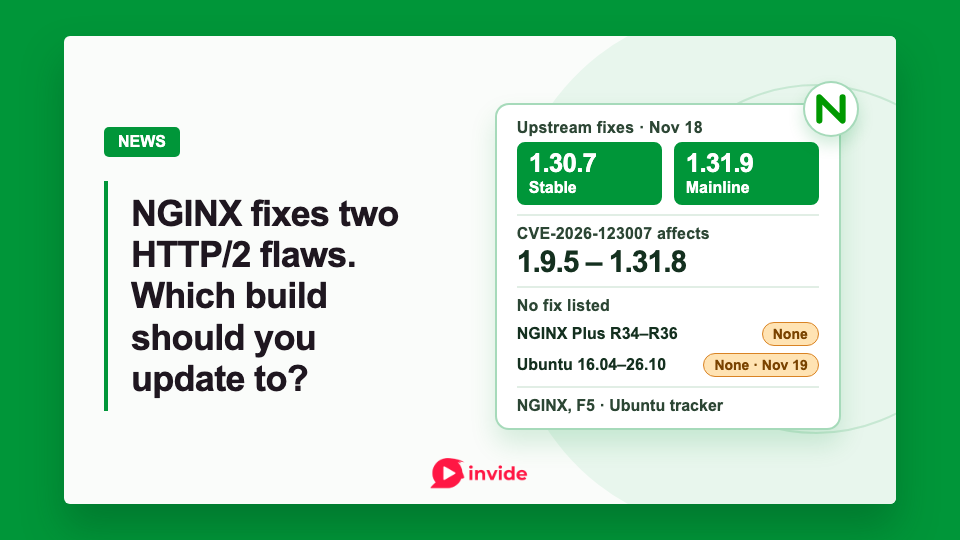
An HTTP/2 flaw in NGINX reaches back to 1.9.5, the release that added HTTP/2 in September 2015. An unauthenticated attacker can use it to run code if address space layout randomization (ASLR) is disabled or bypassed. NGINX released fixes for that flaw and a second HTTP/2 vulnerability on November 18, 2026, in 1.30.7 stable and 1.31.9 mainline. NGINX advisories · NGINX changelog
CVE-2026-123007 affects listeners with HTTP/2 enabled. F5 says the flaw typically crashes an NGINX worker and could allow code execution if ASLR is disabled or the attacker can bypass it. CERT-EU says the code would run with the worker's privileges and needs no authentication. F5 advisory for CVE-2026-123007 · CERT-EU advisory
For CVE-2026-123633, F5 says NGINX must accept HTTP/2 client connections and proxy requests to a backend, and the worker must be running low on worker_connections. F5 gives the same ASLR condition for code execution. F5 advisory for CVE-2026-123633
CERT-EU says researchers demonstrated CVE-2026-123007 and that there were no reports of exploitation in the wild at the time of its advisory. CERT-EU advisory
Which upstream versions contain the fixes?
Update affected upstream stable builds to 1.30.7 or later and affected mainline builds to 1.31.9 or later. NGINX lists 1.9.5–1.31.8 as vulnerable to CVE-2026-123007 and 1.19.7–1.31.8 as vulnerable to CVE-2026-123633. NGINX security advisories
F5 rates both issues High (8.1) under CVSS 3.1 and Critical (9.2) under CVSS 4.0. NGINX assigns CVE-2026-123007 a major severity in its own advisory index. F5 advisory for CVE-2026-123007 · F5 advisory for CVE-2026-123633 · NGINX security advisories
The HTTP/2 fixes are part of a broader release. The upstream announcement lists ten security fixes, including issues in HTTP/3, the resolver and the mail proxy module. CERT-EU's notice covers five vulnerabilities from the F5 disclosure. If you're using that notice to triage the update, check the upstream list for the rest of the fixes in the release. NGINX release notice · CERT-EU advisory
Patch status for NGINX Plus, Kubernetes and distributions
NGINX Plus 37.3.0.1 and 37.0.8.1 cover both HTTP/2 flaws. The first fixes for CVE-2026-123633 were 37.2.0.1 and 37.0.7.1. The later builds on those same branches also fix CVE-2026-123007. F5 lists no fix for affected Plus R34 through R36 releases in either advisory. F5 advisory for CVE-2026-123007 · F5 advisory for CVE-2026-123633
For both HTTP/2 CVEs, F5 lists these product updates. F5 advisory for CVE-2026-123007 · F5 advisory for CVE-2026-123633
| Product | Fixed builds listed | Branches with affected releases and no listed fix |
|---|---|---|
| NGINX Ingress Controller | 2026-lts-r11, 5.8.0 | 3.x, 4.x |
| NGINX Gateway Fabric | 2.9.0 | 1.x |
| NGINX Instance Manager | 2.25.0 | |
| F5 WAF for NGINX | 5.16.2, 5.14.4 | |
| F5 DoS for NGINX | 4.13.0 | |
| NGINX App Protect WAF | None listed | 4.x, 5.x |
| NGINX App Protect DoS | None listed | 4.x |
If your operating system supplies NGINX, check its security tracker for the full package version. A distribution can backport a fix while keeping an older upstream version in the package name. On November 19, Ubuntu listed its NGINX packages for 16.04 through 26.10 as vulnerable to CVE-2026-123007, with no fixed package listed for those releases. Ubuntu security tracker
If you cannot update immediately
CERT-EU recommends patching vulnerable internet-facing instances first. If an update has to wait, it recommends disabling HTTP/2 on exposed listeners as a temporary workaround for CVE-2026-123007 and CVE-2026-123633. Remove the http2 parameter from the exposed listen directives or set http2 off; in the applicable server configuration. F5 lists no mitigation in either CVE advisory. CERT-EU also recommends watching the NGINX error log for entries like worker process ... exited on signal. That line records a worker crash and needs further investigation before it can be attributed to an attack. CERT-EU advisory · F5 advisory for CVE-2026-123007 · F5 advisory for CVE-2026-123633
Keep the patch scheduled even if you disable HTTP/2. The workaround addresses only the two HTTP/2 CVEs. CERT-EU says the HTTP/3, resolver and mail proxy flaws can also lead to code execution, and the November 18 releases include fixes for all three. CERT-EU advisory · NGINX release notice
Member discussion