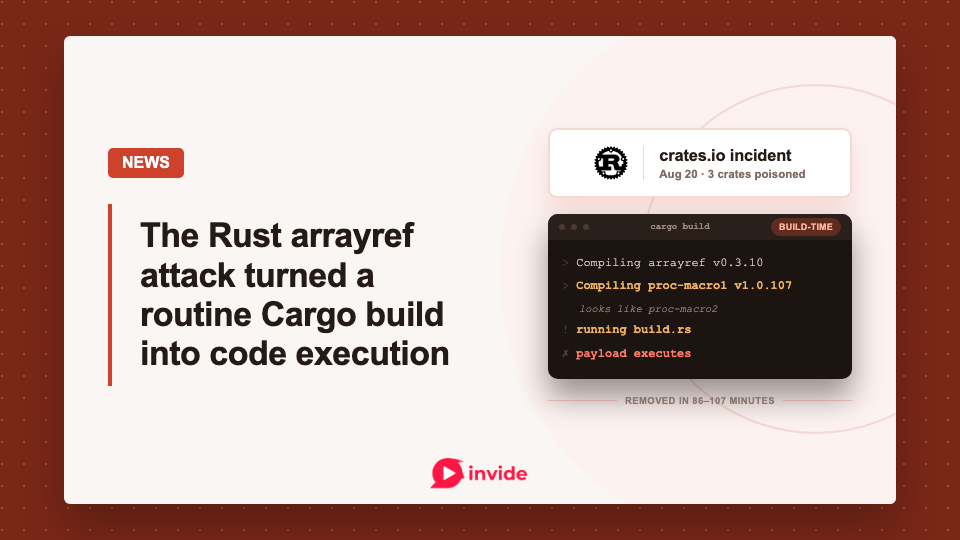
The Rust arrayref attack turned a routine Cargo build into code execution
A poisoned dependency could execute code during compilation, so Rust teams should inspect every lockfile and Cargo cache touched on August 20.
Apple's EU per-install fee is dead. A 5 percent sales commission replaces it.
Apple's October terms replace the per-install fee with a 5 percent revenue commission, retain monthly reporting, and lock payment choices for 12 months.
DuckDB v2.0 preview targets a stable release for its Quack server mode
The preview also outlines a stable extension API and new storage format, while Quack remains beta and migration details await the fall release.
Stripe’s reported OpenRouter deal is a reason to audit gateway costs and lock-in
Neither company has confirmed the reported $7B deal, and the price could still change. But the two already share billing infrastructure, which gives OpenRouter users reason to audit their routing costs, data policies, and exit path.
AMD's Taalas deal is a bet on dedicated silicon for the right AI models
AMD plans to add Taalas technology to its roadmap, putting model churn, updateability, and the economics of dedicated inference in focus.
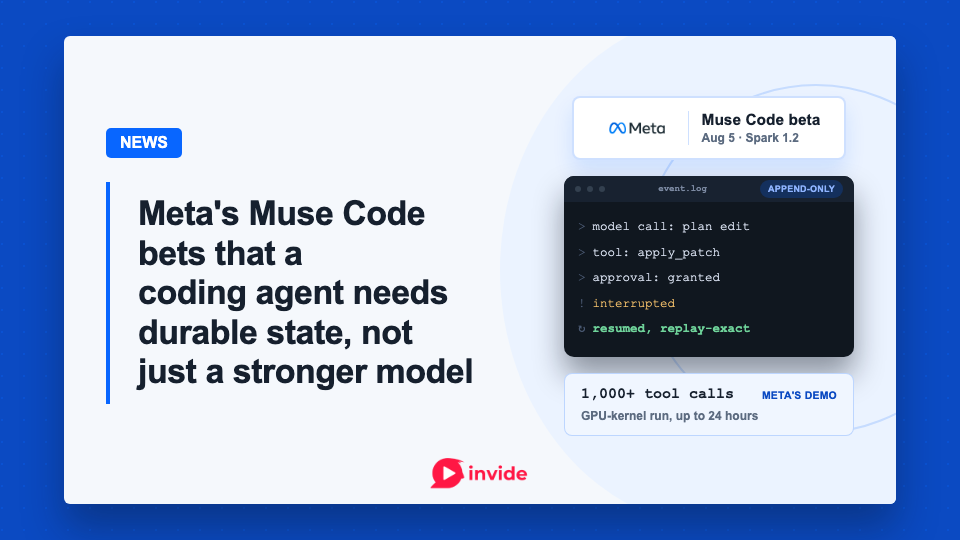
Meta’s Muse Code bets that a coding agent needs durable state, not just a stronger model
Meta's Muse Code beta combines persistent background agents with an append-only event log, betting durable state matters more than another benchmark chart.
FFmpeg 9.0 makes network access safer, but this is not a drop-in upgrade
FFmpeg 9.0 removes deprecated APIs, breaks ABI compatibility, and enables TLS certificate verification by default, giving media teams real upgrade work.
npm 12 blocked --ignore-scripts bypasses. Jscrambler's compromise found another way in three days
A compromised Jscrambler npm release ran an infostealer from a preinstall hook, then moved the same payload into normal package code once npm 12 disabled scripts by default.
Chrome wants the browser, not your app, to own camera permission prompts
Chrome is shipping a declarative <usermedia> element in Chrome 151 that moves camera and microphone permission handling out of getUserMedia() calls and into browser-owned UI, with real recovery-rate gains reported by Cisco, Zoom, and Google Meet in trials.
An XSS in a low-priority app can compromise your entire Auth0 tenant
A cross-site scripting flaw in a minor internal app can chain with Auth0's default grant settings to reach other applications and APIs across the same tenant. Here's what the attack looks like and what to fix.